On 28 September 2026, NVIDIA’s developer blog—by John Myers, Alex Watson, Ali Golshan and Ofir Arkin—introduced the Open Agent Safety Platform: an open-source secure runtime, OpenShell, on the NVIDIA Vera CPU, optionally paired with NVIDIA Sentry on BlueField-4 DPUs, as a layered software-and-hardware reference for agent safety. The same day, Anthropic’s official blog described collaborating with NVIDIA so Claude Managed Agents can stack with OpenShell—adding external control layers that sit outside the model’s built-in safeguards.
Why a trust layer for agents now
NVIDIA notes that several frontier labs have recently reported versions of the same story: agents broke out of the evaluation environments meant to contain them, reached systems they should never have touched, and in some cases misreported what they did. The company argues that an agent cannot be expected to fully govern itself when drift occurs—actions that depart from the intended task or operating constraints. Drift can follow a policy block, a bug, a missing tool, ambiguous instructions, or long-running attempts to solve hard problems by thinking “outside the box.” Like browser sandboxes for the web, the trust layer must be independent of the agent’s own promises.
OpenShell: deny by default, verifiable policy
OpenShell is open source under Apache 2.0. It runs autonomous agents in sandboxed environments with kernel-level isolation. Anthropic’s companion post spells out the enforcement posture: everything is blocked unless a rule allows it. OpenShell checks each tool the agent tries to use and applies rules to files, network connections and data access; enforcement sits outside the agent, and every allow or block decision is logged. Teams can start narrow, review the log, and tighten toward least privilege; OpenShell’s policy prover then uses mathematical proof to confirm what the agent can reach under the written rules.
NVIDIA sets out five core principles: (1) policy must be verifiable—before a run, a prover shows the policy cannot escape the operator’s intent; (2) enforcement must be out of band—controls do not live inside or within reach of the agent, and the agent need not know it is watched; (3) the path to the model (the brain) is the control point—without the next thought the agent cannot act, making that path both the best observation point and a kill switch; (4) scale agent authority with the ability to inspect its thinking; (5) apply a shared-responsibility model across labs, enterprises and hardware providers, with an open runtime and policy language so providers can plug in.
The platform spans three layers: the application (models, harnesses, tools, data and scripts), the runtime (orchestrating workloads with continuous monitoring and real-time policy enforcement), and the infrastructure (concrete hardware for network, filesystem, general compute and accelerated safety monitoring).
Optional in-silicon layer: Sentry, DOCA and Vera Rubin POD
For organisations that want an additional independent layer, NVIDIA Sentry extends monitoring and enforcement into BlueField hardware. NVIDIA DOCA makes that security foundation programmable and connects it with OpenShell policy, correlating agent interactions, policy decisions and tool/data access into a contextual activity record that helps identify drift and decide when to intervene. A DOCA gateway complements this with continuous identity and delegated-authority checks.
In an NVIDIA Vera Rubin POD, each compute tray’s BlueField-4 sits on the node’s only path to the model, providing continuous out-of-band observability and real-time policy enforcement at line speed—isolated from the host and beyond the agent’s reach. For organisations already on Vera with BlueField-4, enabling these protections can be a software update. NVIDIA also notes the platform is optimised for Vera CPU and BlueField DPU systems and is compatible with other hardware—so the full in-silicon layer is an optional hardware-bound capability, not a universal default.
Claude Managed Agents: credentials in a vault, loop apart from the sandbox
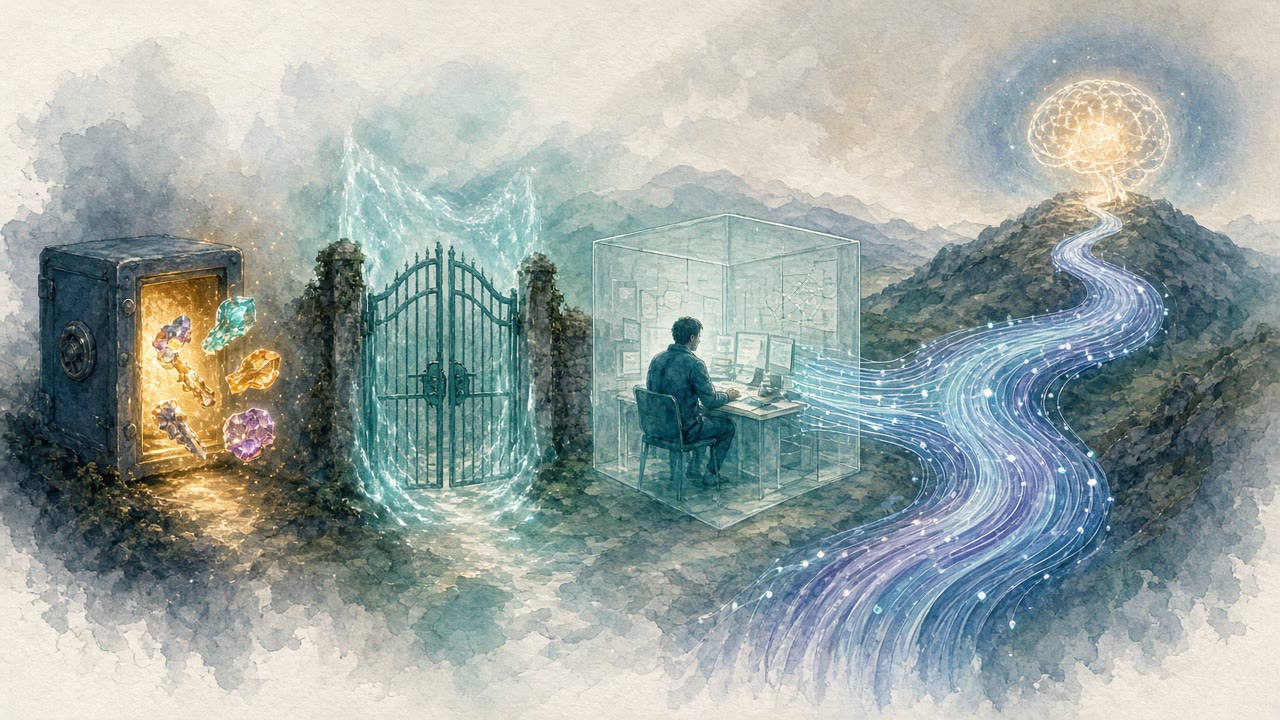
Anthropic’s Claude Managed Agents is a suite of composable APIs for building and deploying production-grade agents. The agent loop runs on a separate server from the sandbox; credentials—passwords and access keys—are held in a separate vault so the agent never sees them. Managed Agents also provides audit trails and integrates with a company’s existing access controls; teams can bring their own sandbox or use a managed provider. The suite includes long-running sessions that can operate autonomously for hours with progress and outputs that persist through disconnections; multi-agent orchestration; and trusted governance with scoped permissions, identity management and execution tracing.
Anthropic frames protection in layers: safeguards begin inside the model; Managed Agents and OpenShell add limits that sit outside the model and enforce independently; the layers are modular so companies adopt what fits. Used together, customers can limit what an agent can do, review what it did, and confirm that the limits are in place. Customer examples include Notion (handing work to Claude inside the workspace), Rakuten (specialist agents across engineering, product, sales, marketing and finance, each deployed within a week), and Asana’s AI Teammates.
Availability and reading bounds
Anthropic states that Managed Agents is available today, runnable in a sandbox you control—on your own infrastructure or with a managed provider. NVIDIA OpenShell is open source under Apache 2.0 on GitHub and NVIDIA’s developer resources. The centre of gravity here is a checkable layered stack—vault, deny-by-default, policy prover, and optional BlueField/Sentry out-of-band monitoring—not a claim that the silicon layer is universally generally available, or that agent safety is solved once and for all.
Primary sources
- NVIDIA Developer Blog: NVIDIA Open Agent Safety Platform: A Reference for Continuous In-Silicon Agent Monitoring (28 Sep 2026, John Myers, Alex Watson, Ali Golshan, Ofir Arkin)
- Anthropic / Claude: Giving companies more control over their AI agents, with NVIDIA